How Machine Learning Works in Cybersecurity, and When the Label Means Something
Why machine learning suits malware defence better than signature files, how to tell real ML from marketing, and how CrowdStrike Falcon applies it.
Nearly every technology vendor now says its product runs on artificial intelligence or machine learning. Marketing teams add the terms because they make a product sound current and ready for the digital economy. Machine learning, though, raises a few questions that buyers should ask before taking the label at face value.
Two questions to ask before buying
The first, and probably the most important, is whether machine learning actually suits the job in hand. A product is not automatically good because it uses machine learning. Equally, an IT product, device or service without AI is not automatically poor. What matters is whether the technology gains something significant from it.
The second is what machine learning really means, and whether the "machine learning" on offer meets the stricter definition. Intelligence that has been programmed in advance and never gets better with experience, for instance, does not qualify.
Genuine machine learning usually starts with some knowledge and experience built in. The defining feature is that it then learns from what it encounters, and it gets smarter without anyone writing new code. These algorithms take in data from everyday experience and use it to make more accurate decisions, to predict outcomes from events and even to get better at tasks such as speech and communication.
Why security suits machine learning
In cybersecurity the claims are not exaggerated. Machine learning fits cyber defence extremely well, and when it is deployed properly it becomes an essential part of any well-rounded security product.
A strong ML algorithm keeps learning as it is given more data, and the more it takes in, the better it becomes at identifying, predicting and deciding. The best algorithms are built to understand one particular kind of information. They generally outperform "broad ML", meaning algorithms designed to handle many different tasks across a wide range of applications. For now, broad AI that closely imitates the human brain remains a distant prospect.
Antivirus used to depend on signature files. To stay protected against the newest viruses, users had to keep those files up to date, which meant the software vendor had to find every possible virus and piece of malware and write a signature for each one, so that regularly updated software could recognise the latest threats.
That model now looks badly out of date. Criminals produce new malware so quickly that a reactive approach cannot keep up. Several sources estimated that in 2017 a new malware variant appeared every 4.2 seconds. At that rate, one vendor writing fresh signature files fast enough is impossible, not merely impractical.
Looked at against the main traits of machine learning, security is arguably an ideal use for it. The huge volume and variety of new malware variants works in the algorithms' favour. The more malware an ML-based defence meets, the more it learns about how malware behaves, and the better it gets at catching new variants nobody has seen before. More attacks, in other words, make the defences stronger. Zero-day attacks can be recognised without waiting for periodic updates.
How CrowdStrike applies it
CrowdStrike builds signatureless machine learning into Falcon, its endpoint security platform. Beyond learning at scale, the company has shaped its ML specifically for security work. It runs fast enough to handle large attacks in real time. CrowdStrike also accepts that ML is imperfect and should form part of a complete strategy. Users can, for example, "train" its ML to suit them, weighing security rules against false positives according to what their company needs.
Attackers keep changing how they operate, and machine learning implemented properly has become an essential element of any serious defence.
More blogs
Why Remote Monitoring and Management Belongs in an MSP's Security Strategy
RMM tools are known for automating IT chores for managed service providers. N-able argues its N-sight platform also closes security gaps for their clients.
Metaverse Security: The Attacks Businesses Expect as They Move Into Virtual Worlds
A Tenable survey of 1,500 security professionals shows how firms entering the metaverse rate the risk of deepfake avatars, eavesdropping and phishing.
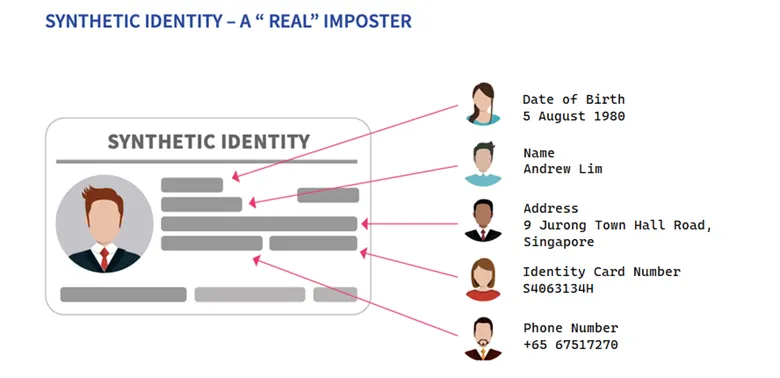
Synthetic Identity Fraud: How It Works and How Institutions Can Catch It
Synthetic identity fraud blends real and invented personal details into a new person. Why banks in Southeast Asia struggle to spot it and what detection relies on.