ESET Uncovers Hodur, a New Korplug Variant Used by Mustang Panda in Ukraine-Themed Espionage
ESET researchers found Mustang Panda using Hodur, a new Korplug variant, in phishing that exploits the war in Ukraine, hitting targets mostly in East and Southeast Asia.
ESET Research has found a cyberespionage campaign, still running at the time of discovery, in which the Mustang Panda APT group uses a Korplug variant that had not been documented before. The operation plays on the war in Ukraine and other news stories from Europe. Its known victims include research bodies, internet service providers (ISPs) and European diplomatic missions, most of them in East and Southeast Asia.
The researchers called the variant Hodur because it closely resembles the THOR variant described in 2020. In Norse mythology, Hodur is the blind half-brother of Thor.
Lures built from the news
Targets were probably drawn in with phishing documents that exploit recent events in Europe, including Russia's invasion of Ukraine. According to the UNHCR, more than three million people have fled the fighting into neighbouring countries, creating a crisis of unprecedented scale on Ukraine's borders. One file linked to the campaign is named "Situation at the EU borders with Ukraine.exe".
Other decoys refer to revised COVID-19 travel restrictions, an approved regional aid map for Greece, and a Regulation of the European Parliament and of the Council. That last one is genuine, taken from the European Council's own website. ESET takes this as evidence that the group keeps track of current affairs and can respond to them quickly and effectively.
Who is behind it and who was hit
Alexandre Côté Cyr, the ESET malware researcher who discovered Hodur, said the company attributes the campaign to Mustang Panda with high confidence, on the basis of code similarities and many shared tactics, techniques and procedures. The group, also known as TA416, RedDelta or PKPLUG, conducts cyberespionage mainly against government bodies and NGOs. Most of its victims are in East and Southeast Asia, though not all, and Mongolia is a particular focus. It is also known for a 2020 campaign aimed at the Vatican.
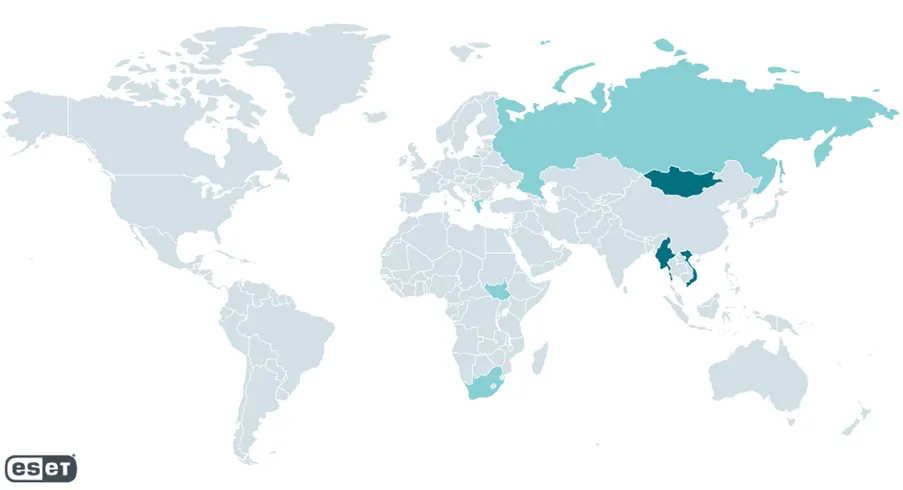
ESET could not determine the sector of every victim, but the targeting appears to match earlier Mustang Panda operations. In line with the group's usual pattern, most victims are in East and Southeast Asia, with some in Europe and Africa. ESET telemetry shows the great majority of targets in Mongolia and Vietnam, then Myanmar, and only a handful in Greece, Cyprus, Russia, South Sudan and South Africa. The sectors identified so far are diplomatic missions, research organisations and ISPs.
Built to frustrate analysis
Mustang Panda often relies on custom loaders for widely shared malware such as Cobalt Strike, Poison Ivy and Korplug (also called PlugX), and it has produced Korplug variants of its own before. Côté Cyr noted that, compared with other Korplug campaigns, this one applies anti-analysis techniques and control-flow obfuscation at every stage of deployment, making the work of malware researchers harder.
ESET has published a detailed technical analysis of the campaign on its WeLiveSecurity blog.