Insecure Cloud APIs: Why They Get Exploited and How to Protect Them
ExtraHop's David Sajoto on why insecure cloud APIs expose data, from weak authentication to tainted open source, and the practices that reduce the risk.
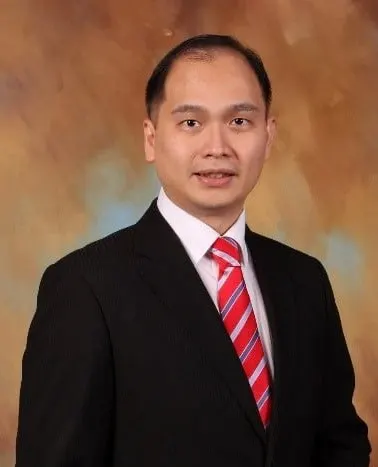 Application programming interfaces (APIs) are supposed to make cloud computing simpler. David Sajoto, vice president for Asia Pacific and Japan at ExtraHop, points out that when they are not secured, they instead widen the attack surface and let people exploit private data. As the world grows more connected, that threat has become harder and harder to overlook.
Open banking is gaining ground across Asia Pacific. Banks and fintech firms, pushing to offer better products and services, are building APIs into their IT infrastructure. Singapore launched API Exchange (APIX), a global platform with an open architecture, to build an ecosystem that "supports financial innovation and inclusion in the region and around the world". Through a strong open banking platform, APIX aims to link organisations with financial institutions and help companies roll out solutions that meet consumers' needs.
Why insecure APIs are a growing threat
More mobile connectivity and heavier app use are drawing more industries into API adoption. Banking leads the way in cloud APIs, but retail, transport and government bodies are also taking them up. That growth attracts attackers looking for ways to abuse APIs for malicious ends.
Sajoto argues that organisations need tighter policies and stricter controls so that cloud APIs do not become a way in for attackers. He cites a recent case in which Singapore's Personal Data Protection Commission (PDPC) fined a ride-sharing company heavily after driver and passenger data was exposed by an API update that had not been tested before release. Any change to systems that could put data at risk, he says, should go through a solid security process to stop unauthorised use of information.
As reliance on APIs deepens, criminals have settled on two common routes to company data.
Weak authentication
The Open Web Application Security Project (OWASP) 2019 report ranks broken user authentication among the leading API vulnerabilities. Some developers build APIs with no authentication at all, which leaves them fully exposed to the internet so that anyone can reach enterprise systems and data through them. Sajoto likens it to walking through a neighbourhood testing doors until one turns out to be unlocked.
Reliance on open source components
Building software from components is now standard practice, and many developers pull open source software into their code to save time. That can expose applications to supply chain attacks. A developer might, for example, download components from public Docker hubs that have been contaminated with cryptocurrency mining code without anyone realising.
Practices that reduce API risk
To prevent data being exposed through APIs by accident or by design, Sajoto recommends that businesses:
- Push developers towards good API hygiene. APIs should be built with authentication, access control, encryption and activity monitoring from the outset, and API keys must be safeguarded and never reused.
- Use standard API frameworks built with security in mind, such as the Open Cloud Computing Interface (OCCI) and the Cloud Infrastructure Management Interface (CIMI).
- Get full visibility across the enterprise security environment. Thorough design policies for cloud APIs do not rule out security problems, so companies should invest in tools that give complete visibility, such as network detection and response, allowing security teams to find and fix API risks quickly.
APIs are expected to become the leading attack vector before long. Because they are central to digital transformation and open a path to sensitive internal data and systems, Sajoto concludes that they deserve their own dedicated approach to security and compliance.