How a Checkbox Approach to Compliance Weakens Cybersecurity Strategy
Rackspace Technology's Sandeep Bhargava explains why ticking compliance boxes falls short and why security belongs in a risk-based framework instead.
Business leaders frequently shape their security policies around what regulators demand, with avoiding fines as the main aim. The result is often a "checkbox mentality": the belief that ticking off compliance rules and escaping penalties is the same as being secure.
The flaw is that compliance moves slowly and predictably, whereas security is dynamic and threats change far faster than any regulation. Meeting a standard such as Singapore's Personal Data Protection Act (PDPA) is a worthwhile step in protecting a business, but it will not hold off skilled attackers who are always searching for sensitive data.
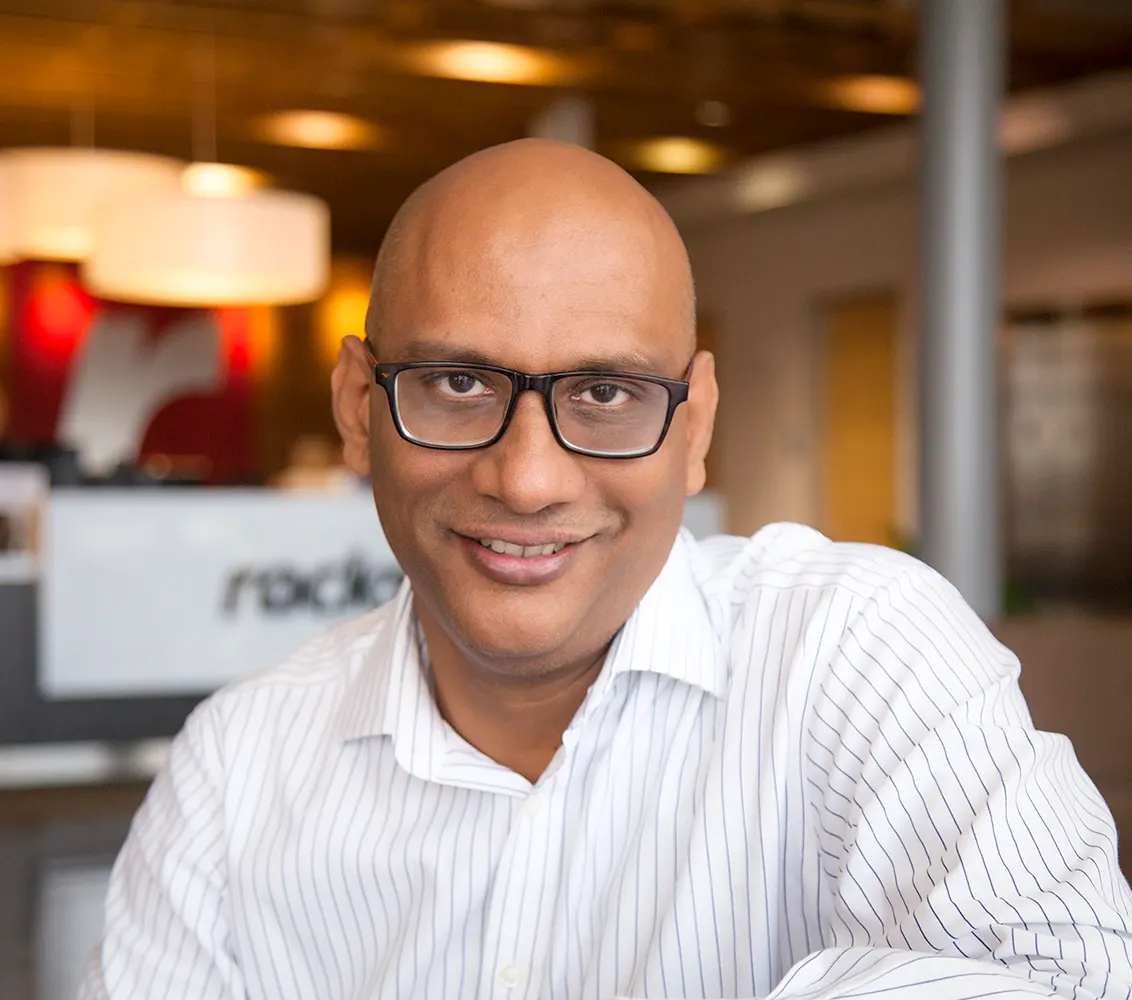 Speaking to CSA, Sandeep Bhargava, managing director for Asia Pacific and Japan at Rackspace Technology, explained where this mindset comes from and why a company that wants to grow and succeed digitally cannot treat cybersecurity as an afterthought covered by a few compliance tools.
Sandeep finds the checkbox mentality interesting because most people apply it in everyday life. Everyone falls into it, he said, because it feels satisfying to write something down, give it context, set out a sequence of steps and then tick each one off like items on a to-do list.
The same habit carries over into cybersecurity. Watching how adversaries adapt and evolve, he said, it is clear that ticking boxes is not the right approach, even though it matches the way people naturally work.
Why compliance alone falls behind
According to Sandeep, cybercrime has grown exponentially in step with technology itself. Each technical advance brings new kinds of crime with it.
In the new normal, organisations keep adopting technologies that will not go away, and every one of them introduces fresh risk. With so many people working from home, security is weaker than it was, and the growing number of successful attacks in the region and worldwide shows criminals are exploiting that.
His advice is for businesses to move past the checkbox mentality so they can keep up with fast-changing threats. Focusing on compliance alone, he says, does little to reduce the full range of risks. Security demands being close to the market and knowing what is going on, constantly refreshing one's knowledge and building a picture of the problems organisations face. From that picture a company can work out what applies to it and how to develop its security posture beyond basic compliance with a guideline.
He therefore urges organisations to keep searching for the right people, those who will think beyond compliance: adaptable, agile and committed to learning and keeping their skills current.
Local businesses that want a stronger security strategy, he added, need to fold their compliance programmes into a risk-based framework. Such a framework concentrates on spotting and dealing with the factors that could cause a failure of confidentiality, integrity or availability. It also considers what applies to a particular company in a particular sector, because risk differs from one industry to another.
Applying a risk-based framework, Sandeep explained, means putting security in the context of the industry, the company and the country. Using it, an organisation analyses those factors, understands and responds to them, and begins to learn what its own risk parameters are.
Obstacles on the way
Strengthening a security strategy will not be free of difficulty. The first hurdle, Sandeep says, is convincing boards to put money into security.
Boards regularly argue over whether spending on particular assets is justified, and security is often one of those assets.
Cyber attacks are increasing, malware is getting better at evading preventive controls, and the risk of breaches grows as more data moves to the cloud. Under those conditions security cannot be set aside.
Without enough budget and backing from management, protecting company data gets harder every year as each employee uses more apps and devices.
Users form another obstacle, according to Sandeep. They do not want security tools to spoil their experience or slow down speed, innovation or performance. Technology teams, similarly, do not want extra security steps to hold up the release of new features.
The final challenge he named is complacency: the belief that "we are well protected" or that everything is under control, followed months or years later by the discovery that some things were never integrated or were simply forgotten.
Where Rackspace Technology fits
Asked whether Rackspace Technology can help organisations avoid these pitfalls, Sandeep said the company is not widely known for security. It came to the field because it sold hosting to customers and needed that hosting to be secure, and its expertise grew from there.
Rackspace then moved on to helping customers migrate to AWS, Microsoft and Google, in single-cloud and multi-cloud setups. As customers started asking how secure the cloud was, the company made a point of building up its knowledge of cloud security.
Sandeep said Rackspace offers a range of assessments that find gaps in a customer's environment and recommend steps to improve cloud security strategy, so the business can meet the security and compliance requirements that matter to it.
The company also runs advanced security monitoring built around a "pod" of security specialists that customers can call on as needed to assess, implement, engineer and manage their security and compliance work. He described the model as agile, proactive and end to end, with security postures improving continuously.
Customers can reach eight or nine different skills through the pod, he explained, buying blocks of 25 or 50 hours and up to 100 hours, and combining the skills they need month by month. "That's where we play, that's where our strength is," he said.
More interviews
Defend Forward: Cybereason and PLDT's CISO on Stopping Attacks Before They Land
Cybereason's Eric Nagel and PLDT and Smart CISO Angel Redoble explain the Defend Forward strategy, the Cyber Defenders Council and why people still decide the fight.
ManageEngine's Subhalakshmi Ganapathy on Data Leaks, Breaches and Adaptive Security in Southeast Asia
ManageEngine's Subhalakshmi Ganapathy explains why Southeast Asian firms are exposed to breaches and leaks, and what adaptive security requires.
Why Data Management Decides How Organisations Survive Ransomware
Veritas's Gary Sievers on rising ransomware in Asia Pacific, the security gap left by COVID-era transformation, and a protect, detect and recover framework.