Why Data Management Decides How Organisations Survive Ransomware
Veritas's Gary Sievers on rising ransomware in Asia Pacific, the security gap left by COVID-era transformation, and a protect, detect and recover framework.
Ransomware has taken the place the data breach used to hold.
Criminals are no longer satisfied with stealing data and then dumping it on the dark web or selling it to whoever pays most. They now prefer to lock the data up and charge for its return. The ransom is usually paid in cryptocurrency, after which both sides move on: the attackers several million richer, the victim several million poorer, and the data restored, provided the criminals keep their word.
Ransomware appears to be spreading in Asia Pacific, and the attacks keep changing shape. That makes them a real concern for organisations across the region, and especially for larger, well-established companies, which in theory can afford bigger ransoms to protect their reputation and avoid long outages.
Smarter attacks, aimed at the biggest payers
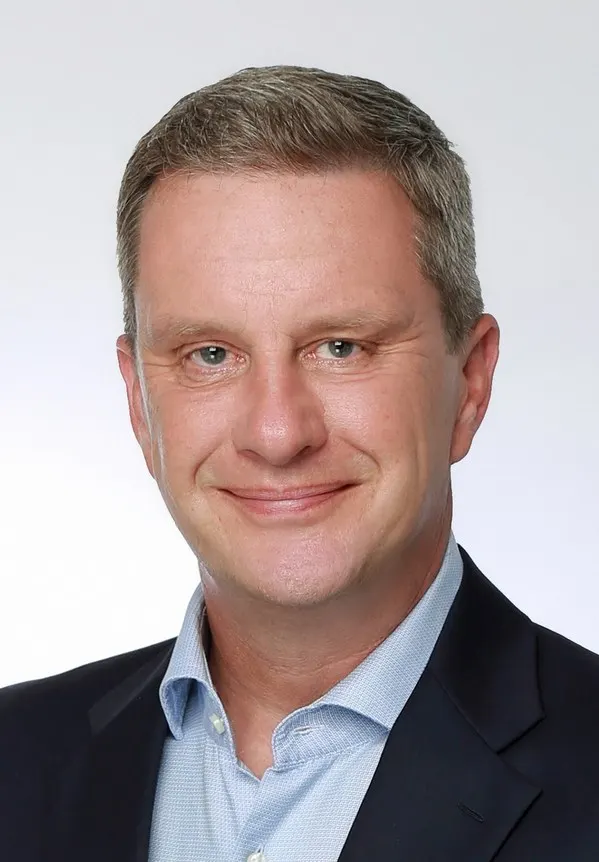 Gary Sievers, vice president of channel sales and alliances for the APJ region at Veritas, says ransomware keeps getting cleverer and more sophisticated, homing in on the organisations from which attackers can extract the most money. Veritas research, he notes, found that the average organisation in Asia Pacific had suffered 2.07 ransomware attacks causing downtime over the previous 12 months.
Sievers sees the regional increase as part of a global pattern in which ransomware has become criminals' preferred method. Many groups are deliberately going after critical industries such as oil and gas, telecommunications and healthcare, and in his words are "attacking data and applications in the cloud and in on-premises systems equally". In Asia Pacific, attackers have used the pandemic as cover to hit hospitals, medical centres and public institutions.
He also points to an incident he believes has not had the attention it deserves: the discovery of malware able to break out of a container and infect a whole cluster. A Palo Alto threat researcher first found it in March and named it Siloscape, and Sievers says it could be used to hold files hostage in a new kind of ransomware attack. For him it shows that attackers are always hunting for better ways to hold data and workloads to ransom, and that organisations need to keep up to date and run a well-configured, secure IT environment.
Digital growth that outran security
The COVID-19 pandemic has sped up both digitalisation and the wider digital transformation of Southeast Asian organisations seeking the best technology available. Bain & Company's report "Digital Consumers of Tomorrow, Here Today" found that the pandemic compressed five years of digital transformation into one year, 2020.
The region now reportedly has 310 million digital consumers, meaning people who buy something online, a figure Southeast Asia had not been expected to reach until 2025. That puts 69% of the population aged 15 and over in this group, and together they have made more than US$85 billion in digital payments. Average digital spending per person in Southeast Asia rose to US$172 last year and is forecast to hit US$429 in 2025, which helps explain why organisations have moved online so fast as well.
Sievers told CSA that the pandemic has changed, possibly for good, how people work, communicate and do business. IT departments have had to speed up their transformation plans to automate more, move workloads smoothly between on-premises and multi-cloud environments and make applications easier to deploy.
Amid all this progress in automation, workload management, cloud adoption and application development, cybersecurity seems to have slipped through the cracks, either ignored altogether or partly misunderstood and so implemented badly. Neglecting it can be disastrous now that ransomware is easier to get hold of than ever, thanks to Ransomware-as-a-Service. Hacks and data breaches are also increasing in the region, including the MyRepublic breach in September and the StarHub incident in July.
According to Sievers, protection infrastructure at most organisations is falling behind: 37% of organisations in APAC say their security has not kept up with transformation projects driven by COVID. Until that infrastructure catches up, he says, they will stay exposed to data-loss events such as ransomware.
Oddly, organisations do understand the ransomware threat and genuinely worry about losing valuable data. Many have still not accepted the need to invest in advanced email security, segmentation and sandboxing, alongside established tools such as next-generation firewalls (NGFW), secure web gateways (SWG) and endpoint detection and response (EDR), to detect, stop and contain ransomware.
Two years to close the gap
Sievers does not expect the region's security infrastructure to catch up quickly. APAC organisations estimate it will take them two more years on average to close the gap opened by COVID-led transformation. Cutting that to one year would require an additional US$2.54 million and 32 full-time IT staff for each organisation. The will to act is there, he adds: 34% of APAC organisations name data management as their top priority for the year.
"Organisations can be sure of two things: That they will face ransomware attacks and that remediation will be required," Sievers said. Knowing this, he argues, lets them improve how they manage information, which benefits both costs and the user experience.
He recommends a framework that supports three parts of an overall security strategy:
- Protect. Data protection has to back up every enterprise workload, including those held in third-party clouds. Encryption, immutable and indelible storage, and zero-trust access are needed at enterprise scale.
- Detect. Threat detection comes next. Automated anomaly detection based on artificial intelligence (AI) is now available and should cover the whole storage environment, backup data included.
- Recover. Recovery needs genuine multi-site resilience that is aware of applications. A trusted platform can automate and orchestrate a full restoration across sites or to the cloud with one click, so that data and applications are both running again.
Veritas's pitch: one platform for scattered data
Sievers also put forward Veritas, which describes itself as a global leader in enterprise data services, as an option for organisations' data management and protection needs. The company offers integrated technology covering availability, protection and insight for businesses of every size.
He described its availability products, including the InfoScale software-defined infrastructure, as keeping mission-critical applications running, reducing downtime and delivering application resilience and storage efficiency across multi-cloud, virtual and physical environments. NetBackup, the flagship data protection product, is meant to extend ransomware protection across the whole enterprise, from edge to core to cloud and from traditional to virtualised and containerised environments.
Veritas's data insight tools and services, among them the Enterprise Vault archiving product and the APTARE IT Analytics platform, give organisations visibility into their data, storage and backup systems so they can get data-related risks under control. Sievers said this is why the world's ten biggest FSI organisations use Veritas.
The hardest part, in his view, is that the data enterprises need to shield from ransomware sits across many platforms, applications and locations. A company may end up buying protection for one platform, then something else for another application or site. "The management burden can quickly grow and grow," he said, and more errors follow.
Veritas's answer is a single platform offering visibility, availability and resilience from edge to core to cloud, with multi-cloud management at scale through a single pane of glass. According to the company, NetBackup supports more than 800 data sources, over 100 operating systems and 1,400 storage targets across more than 60 clouds.
More interviews
Defend Forward: Cybereason and PLDT's CISO on Stopping Attacks Before They Land
Cybereason's Eric Nagel and PLDT and Smart CISO Angel Redoble explain the Defend Forward strategy, the Cyber Defenders Council and why people still decide the fight.
ManageEngine's Subhalakshmi Ganapathy on Data Leaks, Breaches and Adaptive Security in Southeast Asia
ManageEngine's Subhalakshmi Ganapathy explains why Southeast Asian firms are exposed to breaches and leaks, and what adaptive security requires.
How a Checkbox Approach to Compliance Weakens Cybersecurity Strategy
Rackspace Technology's Sandeep Bhargava explains why ticking compliance boxes falls short and why security belongs in a risk-based framework instead.