CrowdStrike's Shawn Henry on Speed, Nation-State Actors and the 1-10-60 Rule in Asia Pacific
CrowdStrike Services president Shawn Henry discusses Asia Pacific threats, nation-state intrusions, big game hunting ransomware and the 1-10-60 response rule.
Attacks on businesses keep growing more sophisticated as technology advances, and security providers are under pressure to answer with more refined forms of protection. With cybercrime forecast to cause as much as US$ 6 trillion in business losses by 2021, many companies are adopting new security and incident response practices to contain fast-moving, advanced threats. Modern attacks are coordinated, efficient and agile, so organisations have to understand the threats they face and be ready to respond when a breach happens.
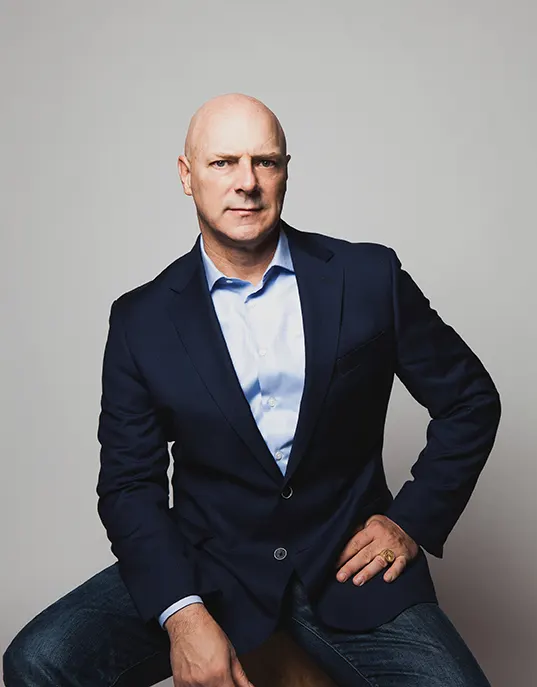
Shawn Henry is President of CrowdStrike Services, where he runs a team of security professionals that investigates and mitigates targeted attacks on computer networks. Under him, CrowdStrike carries out large proactive and incident response engagements in every major commercial sector and in critical infrastructure, protecting sensitive data and networks for companies and governments. Before that he was Executive Assistant Director at the FBI, responsible for all of the bureau's criminal cyber investigations worldwide as well as its International Operations and Critical Incident Response. He has overseen hundreds of major cyber investigations around the world, covering denial-of-service attacks, large bank and corporate breaches and nation-state sponsored intrusions.
CyberSecurity Asean asked him about the threats facing Asia Pacific and how organisations can defend themselves against modern attacks that are more sophisticated and more precisely targeted.
An underserved region where speed decides the outcome
Henry considers Asia Pacific an underserved market for cybersecurity compared with other parts of the world, particularly in its emerging economies. As the region has grown more important to the global economy, high-profile incidents involving critical infrastructure and financial institutions have increased, putting its continued prosperity at risk. A study by AT Kearney singled out Southeast Asia as a prime target for attackers, a trend it expects to continue and which the region's own push to digitalise is feeding without meaning to.
From CrowdStrike's experience, Henry said, speed matters above all when an organisation is handling a breach, and many businesses in Asia Pacific struggle with it. On average an intruder needs one hour and 58 minutes after compromising a machine before moving deeper into the network. That short window is when an organisation has to detect and respond, and reacting quickly is what allows it to contain the intruder and stop the breach.
He added that things are changing fast. Governments are putting cybersecurity near the top of their national agendas, and regulation meant to strengthen cyber resilience is being introduced widely. CrowdStrike is seeing very strong demand for its endpoint products in Australia and across Asia Pacific, and expects that to continue as companies reinforce their defences for a digital-first economy.
Nation-state adversaries in ASEAN and APAC
CrowdStrike's Global Threat report found nation-state adversaries active throughout 2018, going after foreign powers, dissidents and regional rivals to gather intelligence for their decision-makers. North Korea, for example, was engaged in intelligence collection and in schemes to generate currency. The company also tracked OCEAN BUFFALO, an adversary based in Vietnam. Although it appears to concentrate on domestic operations, possibly including internal law enforcement, it may also target Cambodia and has shown activity against the manufacturing and hospitality sectors.
As China and North Korea pursue greater geopolitical standing in the region and beyond, Henry said CrowdStrike expects targeted intrusion groups to keep running campaigns in line with their states' national strategies, seeking information from neighbours and rivals. Their targets include government, defence, think tanks and non-government organisations (NGOs), and they exploit weaknesses in telecommunications and technology companies, managed service providers in particular.
Why firewalls and antivirus no longer suffice
Companies still get breached even with legacy antivirus and layers of security products in place. Almost every organisation breached over the past ten years had both a firewall and antivirus software. Threats are more serious than ever, and most business leaders now accept breaches as an unavoidable cost of doing business, while attackers keep innovating, grow more brazen and treat the endpoint as their first point of attack.
Henry said customers have learned in recent years that relying on single point products does not stop major breaches. Beating a stealthy adversary takes far more than a firewall and traditional antivirus, since every company breached recently had some form of both, and it requires a modern, comprehensive platform. "Cybersecurity is all about speed," he said.
He acknowledged that no single measure stops every attack. CrowdStrike's view is that modern defence rests on strong prevention, backed by the ability to detect and respond within minutes when an adversary does get in, plus proactive monitoring around the clock. According to Henry, that is only achievable with cloud-native endpoint protection and supporting capabilities such as AI, behavioural analytics and threat hunting.
He called for companies to change how they respond to attacks and to review signs of adversary activity in their own networks far more proactively. Monitoring endpoints gives an enterprise the network visibility it needs to catch sophisticated, targeted attacks early. Spotting adversary activity at the endpoint reveals more about attackers' tactics, helps defenders recognise indicators of attack and makes it easier to establish whether a breach has really taken place.
Organisations also need thorough cyber due diligence covering technology, processes and people, which means their security awareness, their processes and the defences around their information systems, products and services. Adversaries are always after the digital assets held on networks, from intellectual property and corporate strategy to customer data. Since desktops, laptops, smartphones, servers and routers can all give a hacker a way in, a single organisation may have hundreds of thousands of endpoints.
Because breakout time is measured in hours, CrowdStrike advises organisations to work to its "1-10-60 rule":
- detect an intrusion in under 1 minute;
- complete a full investigation in under 10 minutes;
- remove the adversary from the environment in under 60 minutes.
An organisation that meets this benchmark stands a good chance of removing the attacker before the attack spreads beyond the first point of entry, which limits the damage and stops it escalating. Doing so calls for investment in deep visibility along with automated analysis and remediation tools, so that responders face less friction, understand the threat and act quickly and decisively. Henry said this is exactly why legacy antivirus and traditional approaches, too slow and ineffective to stop attacks in time, are no longer enough. In his view the answer is a combination of AI and behavioural analytics that can investigate in real time and automate and prioritise threat analysis and response.
Are cybercriminals being held to account?
Henry pointed to progress over the previous year in international cooperation and in making adversaries answer for their actions, including sanctions and an indictment of cybercriminals. Data from the United Nations shows that most economies in Asia Pacific have adopted cybersecurity strategies supported by the necessary legal and operational frameworks, and have set up dedicated agencies to oversee critical infrastructure protection and, where needed, respond to incidents.
He cautioned that more remains to be done, because eCrime groups and nation-state adversaries have shown new flexibility: forming and breaking alliances, switching tactics in the middle of a campaign, and operating within an underground economy that is changing quickly.
One trend he highlighted is the continued growth of ransomware aimed at large organisations, reflecting a shift towards low-volume, high-return crime known as "Big Game Hunting". These campaigns often rely on well-tested tactics, techniques and procedures for reconnaissance, delivery and lateral movement. According to Henry, big game hunters use Advanced Persistent Threat tactics and deploy in a targeted way, compromising credentials, moving laterally and using system administrator tools, behaviour that closely resembles that of nation-state groups and penetration testing teams.
The interview leaves two points on the positive side. Companies that invest in protection beyond traditional antivirus and firewalls, and use AI and behavioural analytics to detect, investigate and remediate breaches, can be well prepared for the attacks ahead. And their own efforts are backed by dedicated agencies around the world working together to hold accountable those who cause major business losses.
More interviews
Defend Forward: Cybereason and PLDT's CISO on Stopping Attacks Before They Land
Cybereason's Eric Nagel and PLDT and Smart CISO Angel Redoble explain the Defend Forward strategy, the Cyber Defenders Council and why people still decide the fight.
ManageEngine's Subhalakshmi Ganapathy on Data Leaks, Breaches and Adaptive Security in Southeast Asia
ManageEngine's Subhalakshmi Ganapathy explains why Southeast Asian firms are exposed to breaches and leaks, and what adaptive security requires.
Why Data Management Decides How Organisations Survive Ransomware
Veritas's Gary Sievers on rising ransomware in Asia Pacific, the security gap left by COVID-era transformation, and a protect, detect and recover framework.