Black Hat Asia 2021: Troy Hunt on How Our Data Leaks Without Us Noticing
In his Black Hat Asia 2021 keynote, Have I Been Pwned founder Troy Hunt explained how breached data spreads and why predictable passwords still fail.
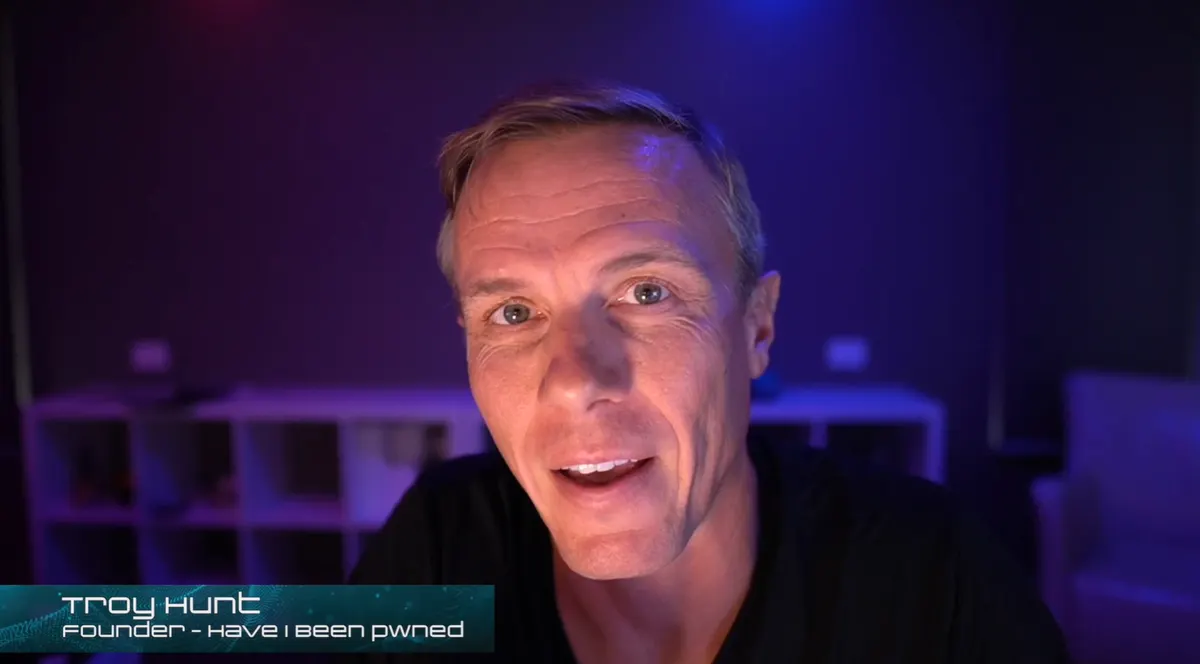
The opening keynote at Black Hat Asia 2021 came from Troy Hunt, the security researcher who founded "Have I Been Pwned", a website where people can check whether their email addresses have turned up in a breach. His session, "Lessons from 11 billion breached records", looked at what lies behind security incidents and how data breaches actually come about.
The pandemic had upended daily life, but it had done nothing to slow the steady rise in security flaws, hacks and breaches, and that was the backdrop to the talk.
The hacker in a hoodie
Hunt began with the way security companies, businesses and the media portray hackers: a figure in a hoodie, alone in a dark room, staring at a green screen. Such images, he said, are chosen to provoke an emotional reaction and have little to do with reality. In his words, "Scary things sell security."
He recalled that when he launched his site, visitors immediately became curious and typed in their email addresses to see whether they had been breached. In doing so they were handing over data to him, which, he joked, he could have used too.
Data escapes from everywhere
On breaches themselves, Hunt argued that data can leak from any source. However carefully people limit what they share or publish about themselves online, the information still finds a way out. He noted that some of the breaches loaded into his service came from organisations that had simply backed up their databases to places anyone could reach.
His own records were a case in point. Hunt discovered his data had been exposed after he gave blood at a donation centre. He had never registered online, but the staff member who took down his details on paper later entered them into an online system, so they ended up exposed as well. Hunt's point was that personal data is already scattered widely, because going about ordinary activities often means handing information over.
Passwords follow predictable patterns
Passwords are the other thing people leak most often. Hunt noted that they have existed since the 1960s and act as a barrier to getting in, so users pick something simple that gets them access quickly, typically a password that is easy to remember and type.
By the 1990s, with the Internet and a growing number of users, passwords had become too easy to guess. Many organisations responded with complexity rules that forced users to build in some variety. Users found simple ways around those rules as well, Hunt said, usually by capitalising the first letter and adding a non-alphanumeric character at the end, most often an exclamation mark.
.webp)
If defenders are aware of these habits, he asked, why would hackers not be? Attackers have long since figured them out. People take predictable shortcuts when creating and memorising passwords, and Hunt believes most still do.
Since passwords are not going away, he said the focus has to be on strength and uniqueness. He called password managers the best answer currently available, noting that besides producing strong and unique passwords they also make everyday tasks quicker.
Hunt also welcomed hardware options such as USB security keys and tokens, which cannot be phished. Their drawbacks are that people have to carry them and they can be expensive to produce, and he expects those hurdles to keep adoption low.
More news
Why Identity Access Management Sits at the Core of Cybersecurity
Security leaders from Bugcrowd, ForgeRock, CrowdStrike, HID, SailPoint, Palo Alto Networks and HashiCorp explain why IAM matters and how to deploy it.
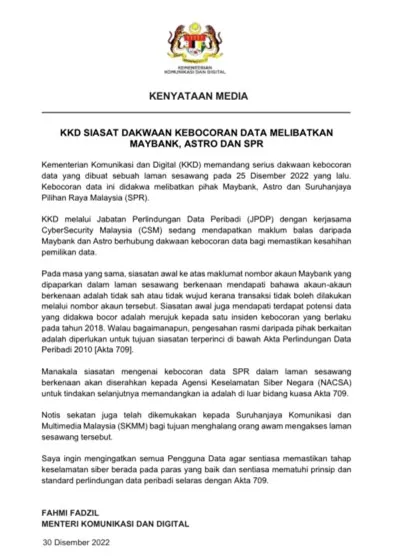
Malaysia's Repeated Data Breaches, Ignorance or Weak Enforcement?
Malaysia keeps leaking citizens' personal data. The 2022 incidents, the limits of the PDPA 2010, how other countries fine offenders, and expert advice.
Cyber Security Asia 2021 Brings Regional Experts Together Online
Cyber Security Asia 2021 ran online over two days in October, opening with CyberSecurity Malaysia's CEO on cyber resilience and a panel on the role of CISOs.